OpenAI Worker Bugged Boardroom, Used Chatbot to Plan It
An OpenAI employee planted a bug in an executive conference room, allegedly using the company's internal AI tools to plan the espionage operation.
👁 113 reads
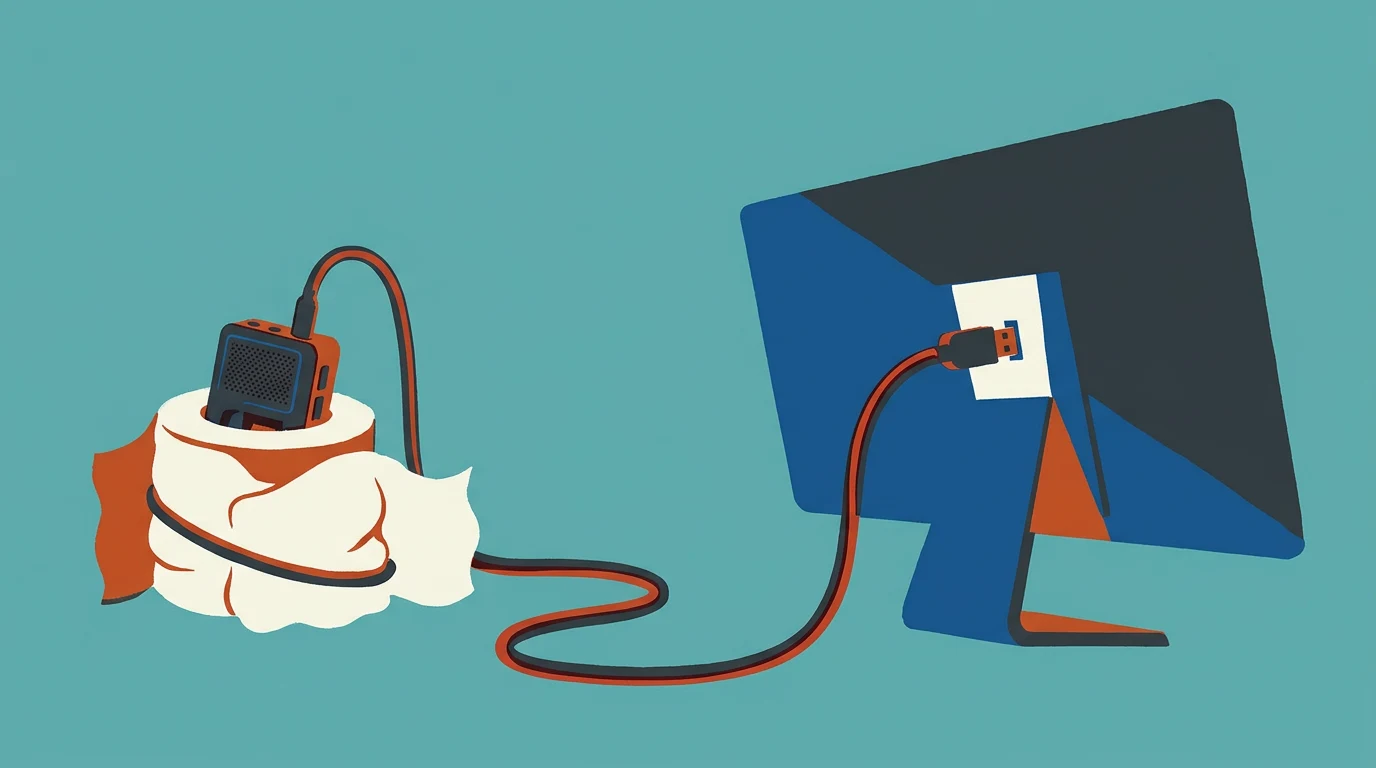
There is something deeply ironic about someone trying to steal trade secrets from an artificial superintelligence lab by leaning on the company’s own AI tools to pull it off. For weeks, Abdulrahman Alfozan queried an internal chatbot and calendar software to lay a trap for his employers. He then wrapped an eavesdropping bug in toilet paper, tucked it behind a display monitor, and powered it via a USB port on a TV inside a boardroom reserved strictly for OpenAI executives.
Had this been the plot of a spy novel, an editor would reject it as implausible. Yet the indictment unsealed on Tuesday describes an entirely real investigation.
The company as an accessory to its own infiltration
Alfozan joined OpenAI in July 2025. Before that, he held roles at a freight logistics startup and at Meta. On LinkedIn, he was also listed as a part-time venture partner at RAED Ventures, a Saudi venture capital fund. Considering the Trump administration signed a bilateral pact granting Saudi Arabia access to advanced AI chips and technologies normally bound by national security export restrictions, that biographical detail is bound to draw intense scrutiny.
The operational details are just as telling. Alfozan did not act on impulse. For several weeks, he used an internal OpenAI productivity agent to monitor calendar schedules for the target boardroom. Simultaneously, he relied on a chatbot account registered in his spouse’s name to ask technical questions about configuring hidden recording devices. He attempted to build a wall between his official work account and his technical reconnaissance, but his operational security fell short.
A conference room reserved for executives
The chosen target was calculated. According to the indictment, the executive suite “can only be reserved by executives and executive assistants.” It hosted “internal leadership meetings,” “technical and product sessions,” and “external briefings” with commercial partners and government officials. Discussions covered highly sensitive matters, including core research, product roadmaps, and government relations.
FBI Director Kash Patel stated that Alfozan sought to “surreptitiously intercept sensitive communications regarding the company’s superintelligence technology.” OpenAI took a more guarded stance: “We currently have no indication that this individual improperly accessed model weights, source code, or customer data,” the company posted on X. His ultimate motive has not been officially confirmed.
On September 30, 2026, during a routine counterintelligence sweep, OpenAI’s security team spotted the gadget wrapped in toilet paper, wedged behind a screen, and plugged into a TV’s USB port. The company described the setup as “advanced.” Investigators found a second recording device in Alfozan’s bag. He was dismissed from his job on Friday, the day of his arrest. On Tuesday, he appeared before the US District Court in San Francisco on one count of using an electronic, mechanical, or other device to intercept oral communications. He faces up to five years in prison.
Google · Your sourcesQuantslant higher in your Google - one clickAdd to preferred sources →What this reveals about AI security
It is tempting to treat corporate espionage as tabloid intrigue: a rogue engineer, hidden hardware, and high-stakes geopolitical jockeying. What stands out to me is how Alfozan managed to consult internal AI systems for weeks to organize an unlawful operation before raising any internal alarms. OpenAI builds tools designed to match and surpass human cognitive work. Yet an internal productivity assistant acted as an unwitting handler for an insider threat.
This is not proof that AI is malicious. It simply demonstrates that tools remain entirely indifferent to user intent, a truth that resurfaces in new disguises with every technological shift. This time, it took the form of a worker carrying electronics wrapped in toilet paper, spending weeks asking an internal bot when executives would next gather.
OpenAI now faces two distinct problems: the criminal case before the court and a reputational challenge that no legal filing can easily erase. For a company assuring regulators and enterprise partners that its operational security is unmatched, the fact remains that a counterintelligence sweep on September 30 caught a bug planted no earlier than September 28. Two days. That was all it took for an unauthorized bug to sit operational at the center of the organization.
More on this from QUANTSLANT


 news·PoeLLM Malware: A GitHub Poem Controlled 3,400 AI ServersPoeLLM used four words in a GitHub poem to find its command server, then mined cryptocurrency on more than 3,400 exposed machines.